DIFC Reg 10
Run DIFC Regulation 10 on every AI system you operate.
regulation10.ae is the compliance plane for firms under DIFC Regulation 10. You add a system, we run the checks, you keep the proof.
Problem
Why this is hard
DIFC firms must show how each AI system is run. The Commissioner can ask for proof. A clean assessment, a clear notice, and a signed audit trail is that proof. We make it on the day you ship the system.
- For DIFC firms that run AI systems
- DIFC Regulation 10 asks for proof
Every autonomous system in scope must be declared
Regulation 10 applies to autonomous and semi-autonomous systems that process personal data in or from the DIFC.
DIFC Data Protection Regulations, Regulation 10
A named officer answers for it
You must appoint an Autonomous Systems Officer and record who signed off each system and when.
DIFC Regulation 10.2
The Commissioner can ask for the proof
You have to produce the assessment, the notice and the trail. Saying you complied is not enough.
DIFC Data Protection Law 2020
What happens to a system
Classify
Risk class and duties
Prove
Assessment, notice, sealed trail
Monitor
Live estate, drift and incidents
File
DIFC filing
Product
How it works
Where the information goes, and what comes back.
- Step 1: Your AI systems. The models and services you run. Your cloud account.
- Step 2: Out-of-band capture. Taken beside the workload, not on the request path. Your cloud account.
- Step 3: Classify and draft. Risk class, duties and citations under DIFC Reg 10. regulation10.
- Step 4: Tamper-evident record. Each decision is hashed into a chain. regulation10.
- Step 5: Evidence pack. One signed export, ready when a regulator asks. Yours to hand over.
Continuous capture is Sentinel, a closed beta on the Enterprise and Sovereign plans. It is not open to enrol yet.
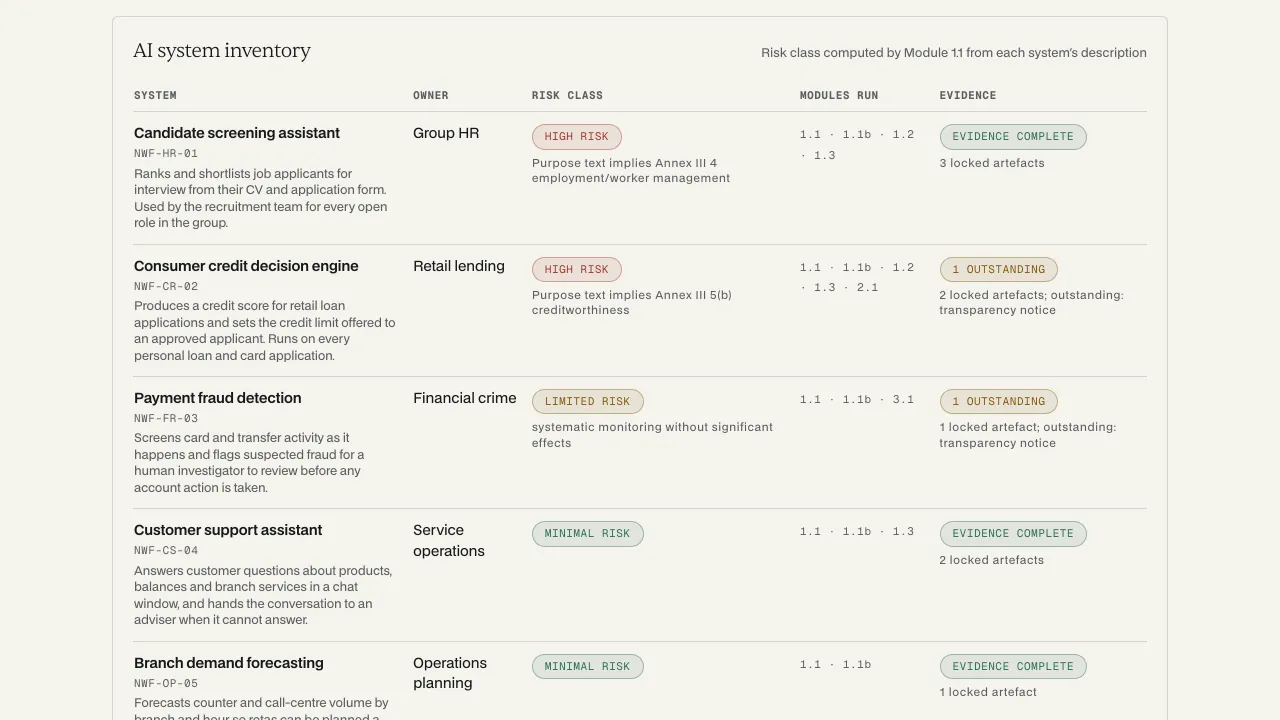
- Classify
Know the risk class before you build
Describe a system and get its DIFC Reg 10 risk class, the duties that follow, and the citation behind each one. It takes seconds and needs no signup.
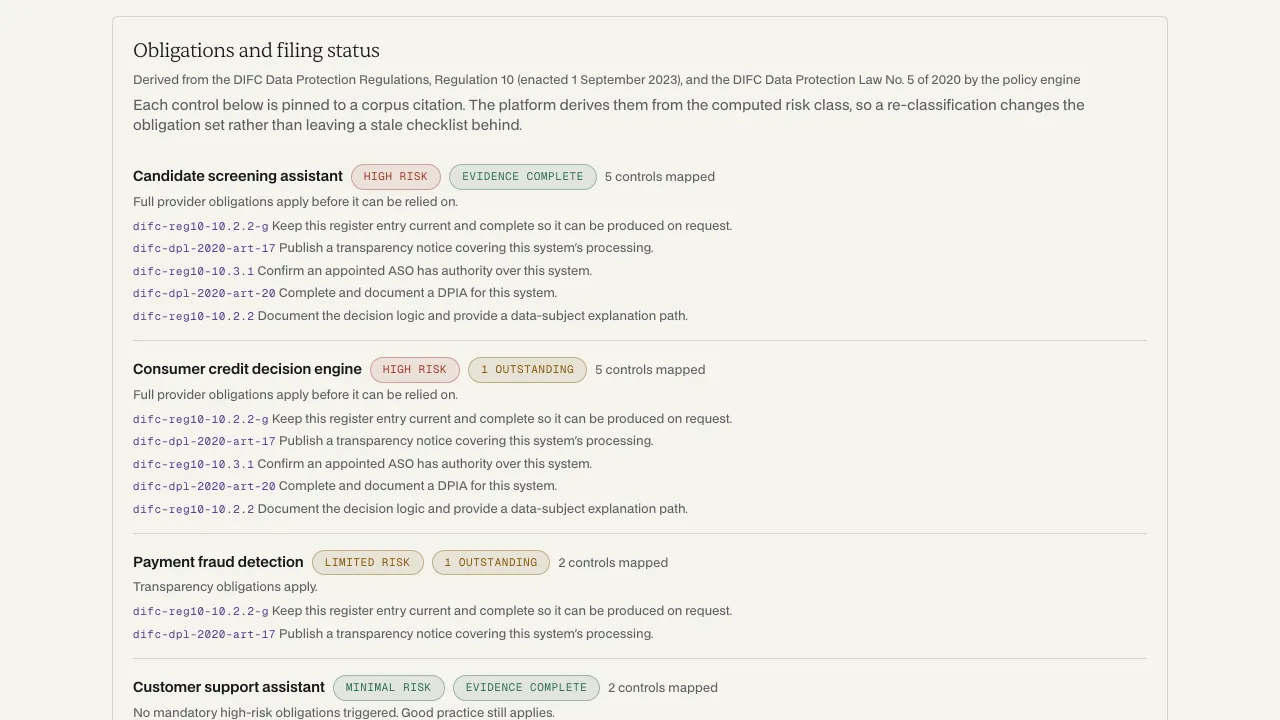
- Prove
Turn the work into evidence
We draft the assessment and the transparency notice, then seal each decision into a tamper-evident trail. You hand over one signed pack.
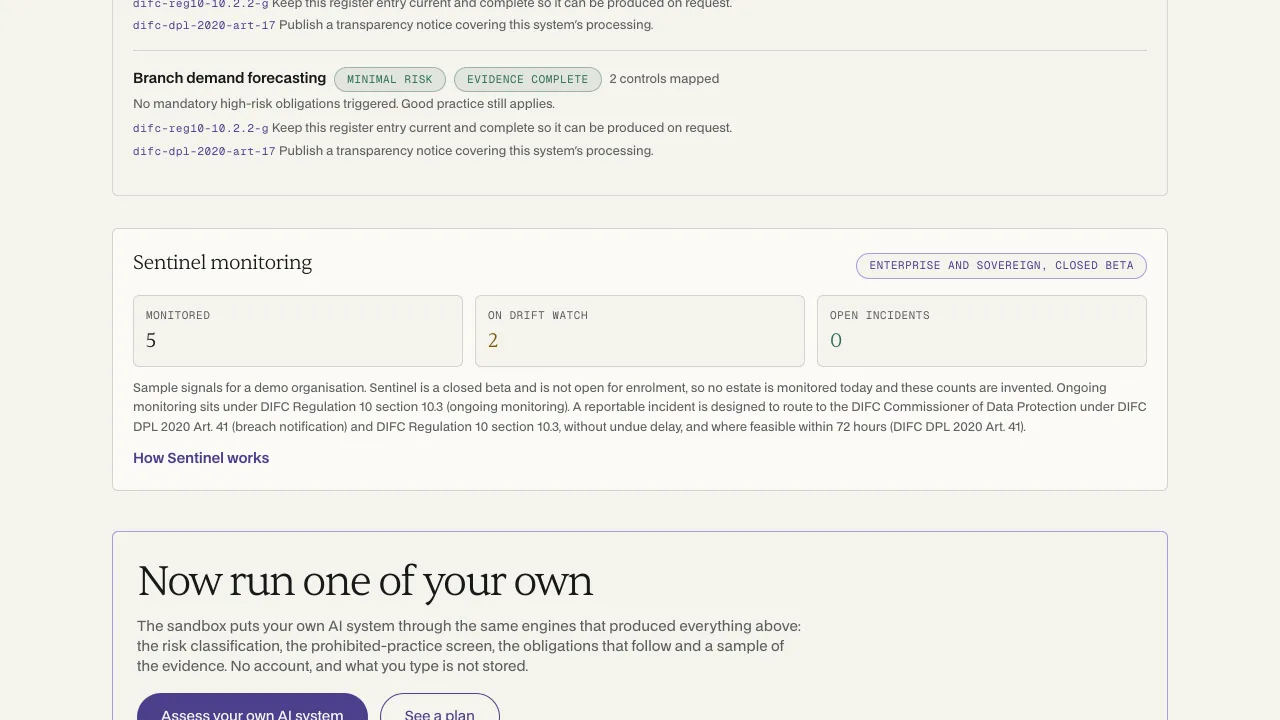
- Monitor
Watch it while it runs
Sentinel is built to watch an estate and raise the filing when something changes. It is a closed beta, not open for enrolment yet.
What each capability gives you
- Risk classification. Know which duties apply before you build, not after an audit.
- Assessment generator. Draft the DIFC Reg 10 assessment your reviewer expects, not from a blank page.
- Transparency notices. Meet the notice duty in plain words your users can read.
- Bias and security checks. Find fairness and security gaps before the system ships.
- Tamper-evident audit trail. Keep signed proof of each decision, ready on the day you are asked.
- Evidence pack. Hand over one signed pack, not a scramble to gather proof.
- Framework cross-walk. Reuse one control set across ISO, NIST, and OECD.
Solutions
The sectors this is built for
Banking
Professional services
Insurance
Legal
Proof
Why you can rely on it
Evidence-grade audit trail
Each decision is hashed into a chain and checkpointed, so a later edit shows up. The trail is exportable for an auditor.
Stated data residency
We name the region your data sits in and the one narrow processing step that runs elsewhere. The detail is below.
Regime-correct filing
We route a filing to the DIFC route the regulation sets, not to a generic form.
We publish what we cannot yet prove
The trust page dates every piece of evidence we hold. It names the gaps we have not closed, and the claims our own probes cannot yet establish.
Where your data lives
Your data resides in Azure's UAE North region. One narrow processing step, the classification and redaction check that screens a prompt before any response is returned, runs on an Azure OpenAI deployment in Sweden Central, an EU/EEA region. That step processes text in flight only; no prompt or response content is stored there. Your data is encrypted in transit and at rest.
References
Customer references
We have no published customer references yet, and we will not invent one. Read the full position
Get started
Assess your AI system
Describe one system and see its risk class, the duties that follow, and the evidence you would need. No signup.
Assess your AI systemStart onboardingor see a plan
No signup for either. The demo runs on sample data.